
35+ WordPress Hacking Statistics & Security Data (2026)

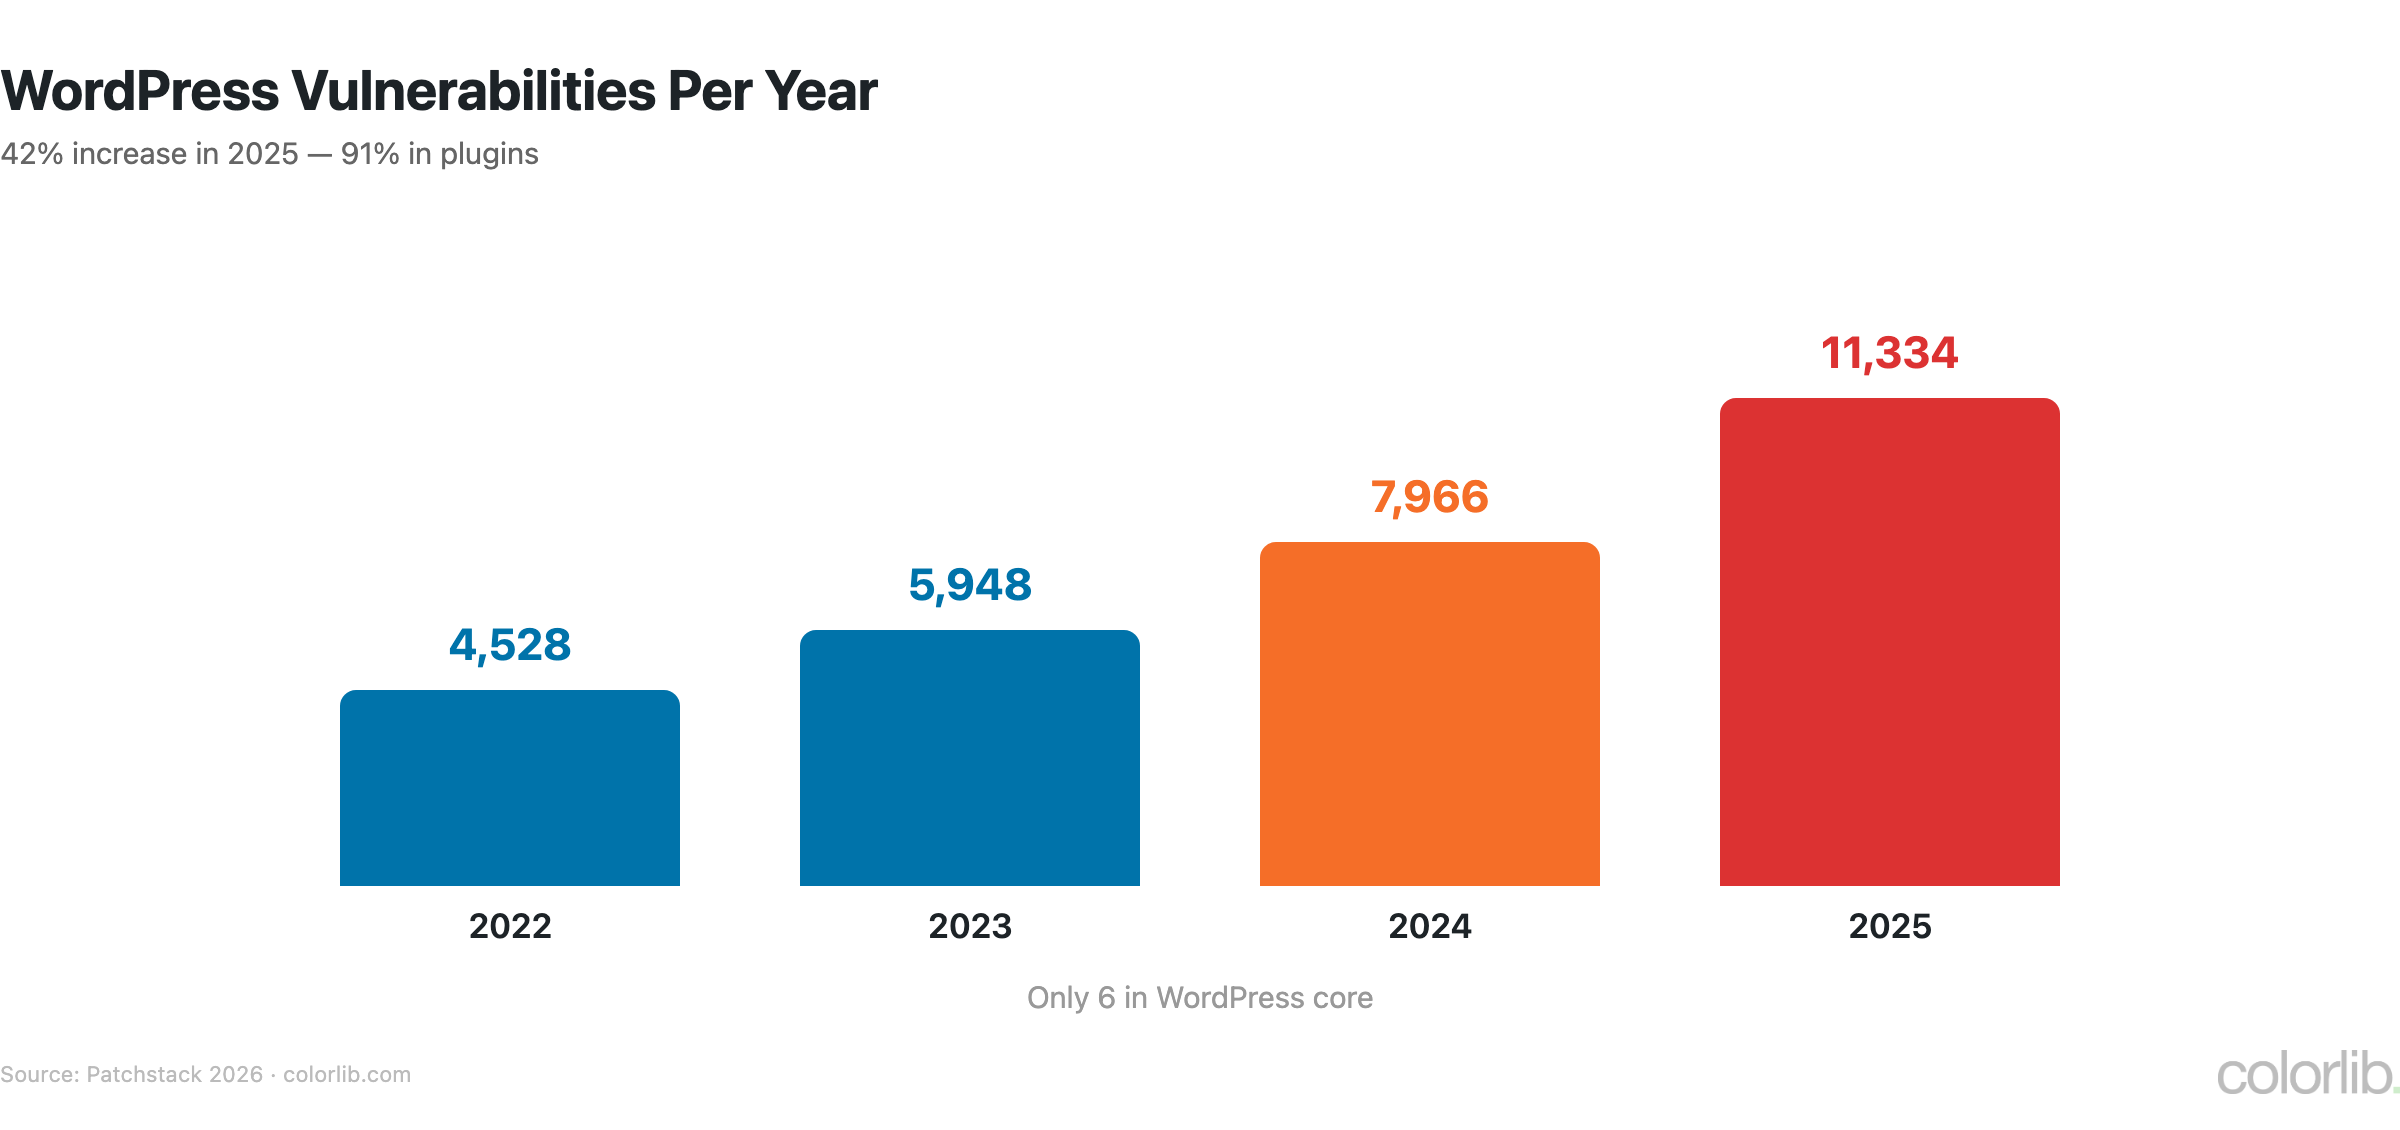
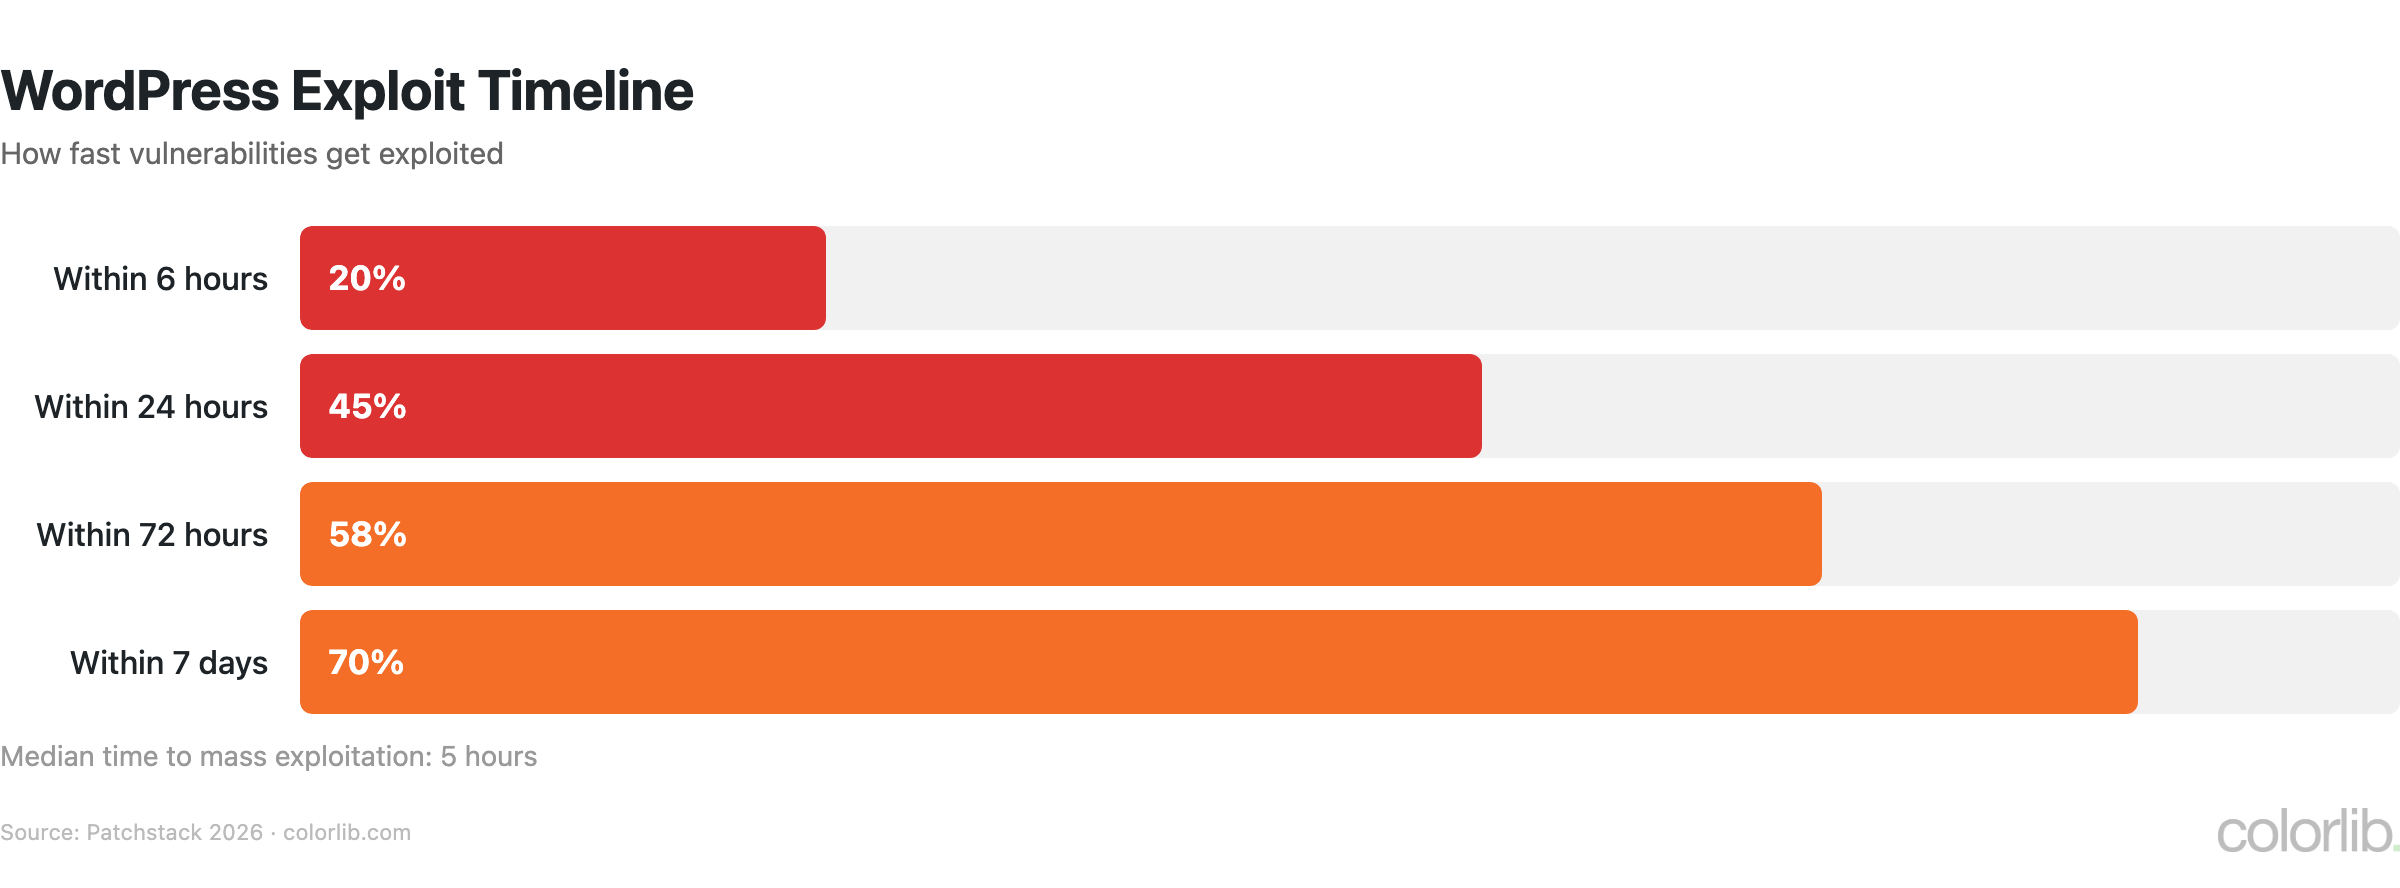
11,334 vulnerabilities in a single year. 91% in plugins. Exploits launching within 5 hours. Here are 35+ WordPress security and hacking statistics from Patchstack’s 2026 report — the data every WordPress site owner needs to see.
Key WordPress Security Statistics (2026)
- 11,334 vulnerabilities discovered in 2025 — up 42% YoY (Patchstack)
- 91% of vulnerabilities are in plugins; only 6 in WordPress core
- Median time to mass exploitation: 5 hours
- 46% unpatched at time of disclosure
- 43% of vulnerabilities found in 2024 required no authentication (Patchstack 2025 report)
- Traditional defences blocked only 12% of WordPress-specific attacks in Patchstack’s 2025 pentests
WordPress Vulnerability Trends
- Vulnerabilities tracked in the Patchstack database: 53,000+ (Patchstack)
- 333 vulnerabilities disclosed in a single weekly report in January 2026, about 48 a day (Liquid Web)
- Highly exploitable vulnerabilities increased 113% YoY in 2025
Vulnerability Breakdown
Exploit Timeline
Critical insight: 46% of vulnerabilities had NO developer patch when disclosed. You can’t rely solely on updates — you need proactive security (WAF, monitoring, minimal plugins).
WordPress Security Practices
- Traditional defences blocked only 12% of WordPress-specific attacks in Patchstack’s 2025 pentests
- 43% of vulnerabilities found in 2024 were exploitable without authentication
- AI models introduced a security flaw in about 44% of code-generation tasks (Veracode 2026)
- ~2.6% of WordPress sites run version 4.x or older — severe security risk (WordPress.org)
- Only ~62% run a PHP version with active security patches (PHP 8.2 or newer)
Key Takeaways
Sources
Frequently Asked Questions
How many WordPress sites get hacked?
With 11,334 vulnerabilities discovered in 2025 and exploits launching within 5 hours of disclosure, thousands of WordPress sites are compromised daily. The exact number isn’t tracked globally.
Is WordPress secure?
WordPress core is very secure — only 6 vulnerabilities in 2025. The risk comes from plugins (91% of vulnerabilities) and outdated installations. A WordPress site with minimal, updated plugins and proper security is as safe as any platform.
What causes most WordPress hacks?
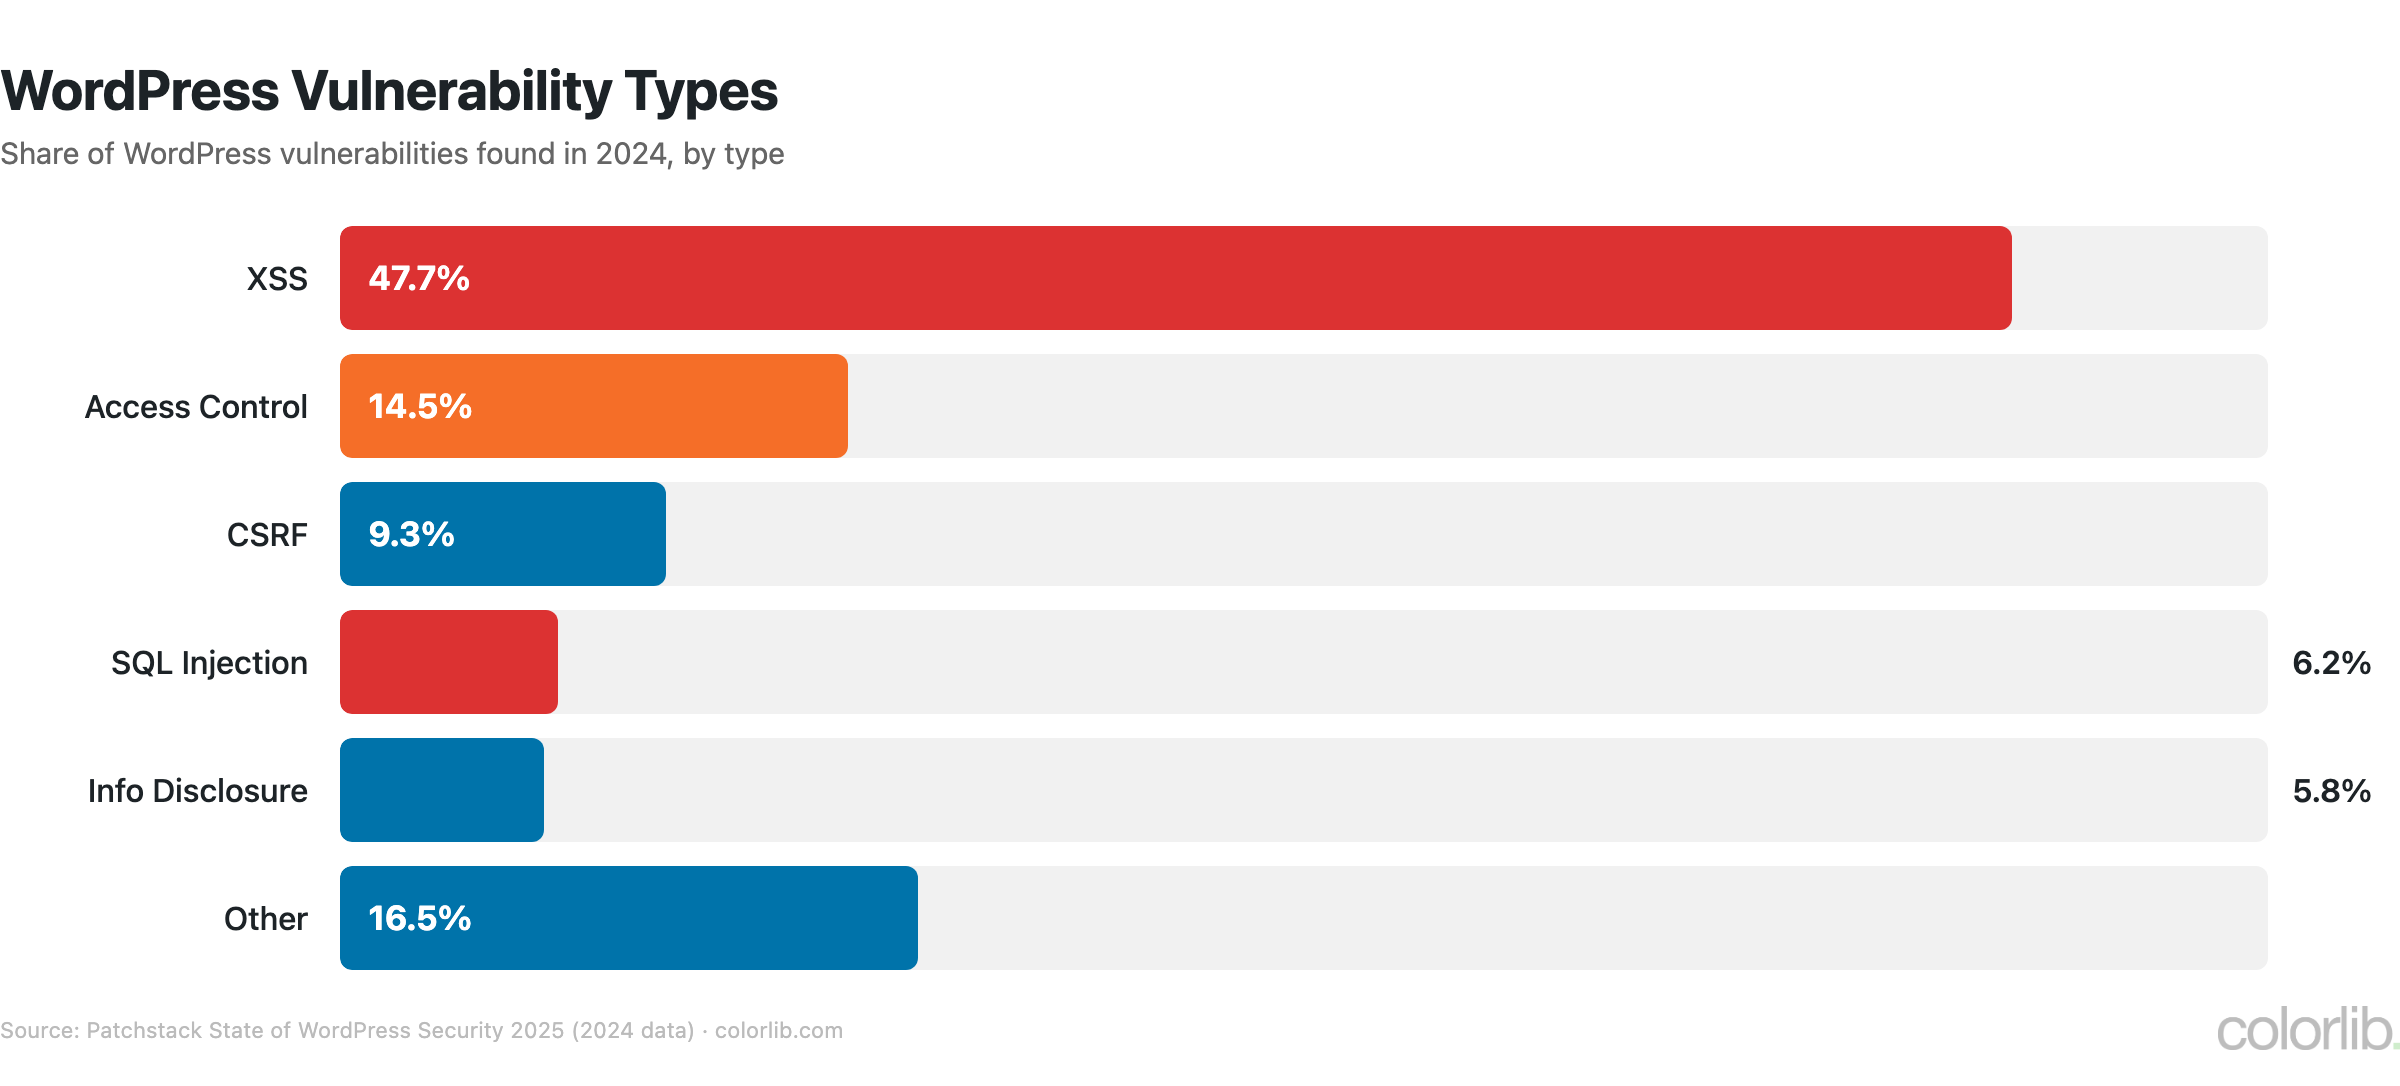
Vulnerable plugins cause 91% of WordPress security issues. XSS (cross-site scripting) was 47.7% of vulnerabilities found in 2024, and 43% of them could be exploited without any authentication. In 2025, Broken Access Control was the most exploited type.
For broader cybersecurity data, see our Hacking Statistics and Password Statistics. For WordPress help, browse our WordPress Statistics.
Was this article helpful?
YesNo

